How to Respond to Negative Patient Reviews Without Breaking HIPAA
You can respond to a negative patient review, but the moment your reply confirms someone was your patient or mentions any detail of their care, you risk a HIPAA violation, and regulators have fined practices thousands of dollars for exactly that. The safe response says nothing about the individual, discloses no protected health information, and moves the conversation offline. It sounds simple, yet the instinct to defend yourself by explaining "what really happened" is precisely what lands practices in trouble. This guide covers the one rule that matters, the real enforcement actions that prove it, a response template you can reuse, and the mistakes that turn a bad review into a compliance problem. It is written for doctors who want to protect both their reputation and their license.
The one rule that governs every reply
The HIPAA Privacy Rule does not stop you from responding to reviews or being active online. What it stops is the disclosure of protected health information without the patient's written authorization. That single rule governs everything about how you reply.
Protected health information, or PHI, is any information that identifies a patient and relates to their health, care, or payment for care. The trap for doctors is that this bar is far lower than it feels. Simply confirming that the reviewer was your patient is itself a disclosure, because it links an identifiable person to the fact that they received care from you. You do not need to mention a diagnosis to cross the line. Writing "we treated you fairly during your visit" already acknowledges a treatment relationship, and that acknowledgment is the disclosure.
This is why the defensive reply is so dangerous. A reviewer complains, and the natural urge is to correct the record: they missed appointments, they were difficult, the procedure went fine. Every one of those rebuttals confirms the person was a patient and reveals something about their care, and consent to that disclosure was never given. The reviewer waived nothing by posting. The rule protects them regardless of what they said about you.
The penalties are real, and they are recent
This is not a theoretical risk. US regulators have pursued and penalized practices specifically for disclosing patient information in review responses, and the amounts are not trivial for an independent practice.
The Office for Civil Rights, which enforces HIPAA, settled with a New Jersey psychiatric practice, Manasa Health Center, for $30,000 after it disclosed patient information, including details of diagnosis and treatment, in responses to negative online reviews. In related enforcement, a dental practice reached a $23,000 settlement, and a dental practice in North Carolina was hit with a civil monetary penalty of $50,000 for disclosing PHI when responding to a patient's review. The OCR Director put the position bluntly, saying that providers disclosing patients' protected health information online in response to negative reviews is simply not allowed.
The pattern in these cases is consistent and instructive. None of the penalized providers set out to breach privacy. They were stung by a review and responded by explaining their side, and the explanation contained PHI. The enforcement makes clear that a wounded, detailed rebuttal is not just bad public relations, it is a regulatory exposure that has cost real practices real money.
The safe response, with a template
The good news is that a compliant response is not only safe, it usually reads better to prospective patients than a defensive one. The formula is to acknowledge, stay generic, and move offline, without ever confirming a treatment relationship.
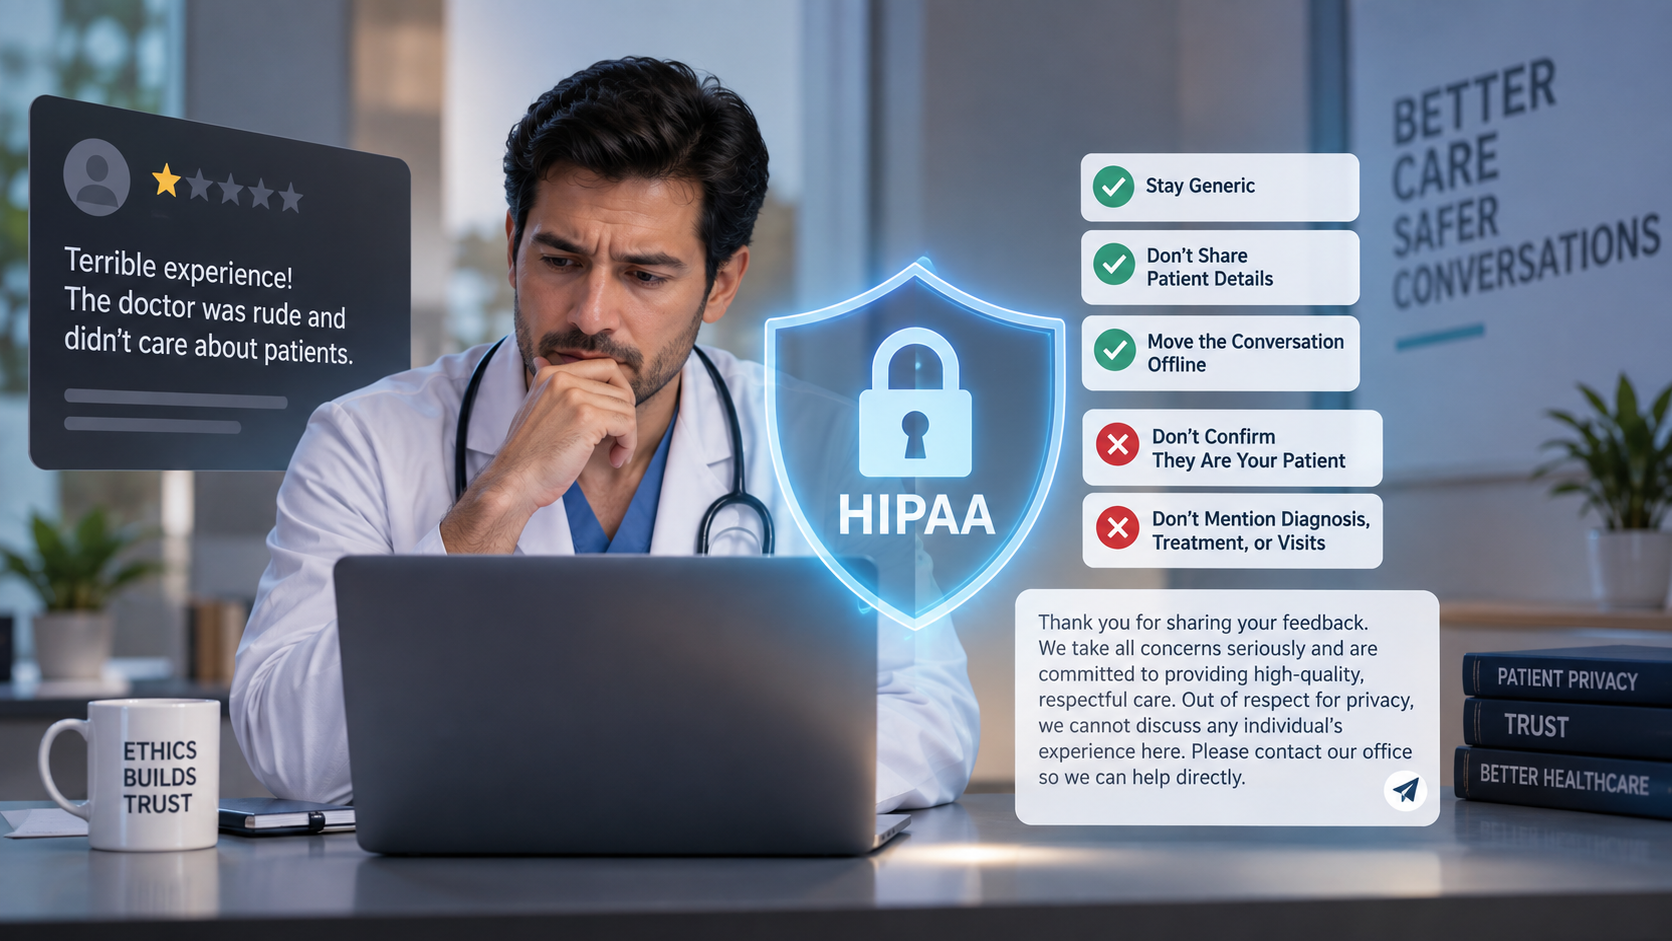
A reusable structure looks like this: thank the reviewer for the feedback in general terms, state your practice's commitment to good care and privacy, note that you cannot discuss any specifics publicly, and invite them to contact the practice directly to resolve concerns. A concrete version reads: "Thank you for sharing your feedback. We take all concerns seriously and are committed to providing high-quality, respectful care. Out of respect for privacy, we cannot discuss any individual's experience here. Please contact our office at [number] so we can help directly." Notice what that reply never does. It never confirms the person was a patient, never references any visit, and never touches care details.
That single template handles the vast majority of negative reviews. The prospective patients reading it see a practice that is calm, professional, and privacy-conscious, which is often more reassuring than the complaint is damaging. A measured non-answer that protects privacy signals competence. A detailed rebuttal signals defensiveness and, worse, may break the law. The relationship between how you handle criticism and whether patients trust you is part of the broader picture in the patient star-rating threshold.
What must never appear in a public reply
A short list of specifics turns a normal reply into a violation. Commit these to memory, or better, to a policy every staff member follows.
Never confirm the person was a patient, because that acknowledgment alone is a disclosure. Never mention any clinical detail, including the type of visit, the treatment, the diagnosis, or the outcome, even to say the care was appropriate. Never reference dates, appointments, payments, or insurance, since these are also identifying and care-related. Never correct the reviewer's version of clinical events, however unfair it feels, because the correction itself reveals PHI. And never let a frustrated staff member reply in the heat of the moment, since most violations happen when someone responds emotionally rather than following the policy.
The discipline is to treat every public reply as if the reviewer is a stranger you have never met, because legally you must speak as though you cannot confirm otherwise. Everything specific belongs offline, in a direct conversation where, if appropriate, you can obtain consent. If a review is defamatory or fake rather than a genuine unhappy patient, the route is the platform's removal process or legal advice, not a public rebuttal that risks your own compliance.
Beyond the single reply: managing the pattern
One good response protects you legally, but reputation is built on the pattern, not the single reply. A negative review does the least damage when it sits in a healthy, active profile rather than a thin, stale one.
The most reliable protection against any one bad review is volume of genuine recent reviews, which dilutes an outlier and keeps your average above the threshold patients screen on. A single one-star review is devastating on a base of ten and negligible on a base of a hundred, which is the direct link explored in how many Google reviews a clinic needs to rank. Keep your listings consolidated as well, so responses and reviews attach to one strong profile rather than scattering across duplicates, a hygiene issue covered in the NAP audit. Together, a compliant response, a steady flow of honest reviews, and clean listings turn negative feedback from a crisis into a manageable, occasional event.
A note for clinics in India. The same caution applies, and if anything the rules are stricter, because the Indian medical ethics regulations bar displaying or soliciting patient testimonials and prohibit disclosing patient information. Respond in the same generic, privacy-protecting way, never confirm a treatment relationship, and keep all specifics to a private channel. The principle is identical in both markets: protect patient confidentiality first, defend your reputation second, and never let the second compromise the first.
A step-by-step workflow for every negative review
Turning the rule into a routine is what actually prevents violations, because the danger is emotional, in-the-moment replies. A fixed workflow removes the emotion. Here is one any practice can adopt.
First, pause. Nobody replies to a negative review on the day it appears without a second person reviewing the wording. This single rule prevents most breaches, because the worst replies are the fast, wounded ones. Second, decide the category. Is this a genuine unhappy patient, a case of mistaken identity, or an abusive or fake review? Genuine complaints get the generic template, mistaken-identity and fake or policy-violating reviews go to the platform's reporting process instead. Third, draft from the template rather than from scratch, so the reply never accidentally confirms a treatment relationship. Fourth, have a second trained person check the draft against a short list: does it confirm the person was a patient, mention any care detail, reference any date or payment, or correct their clinical account? If any answer is yes, rewrite. Fifth, post the approved reply and, where appropriate, follow up privately through a phone call or secure channel where consent and specifics can be handled properly.
Five steps, applied every time, convert review responses from a liability into a controlled process. The workflow matters more than any individual's judgment, because it protects you on the day someone is angry and not thinking clearly.
Training the people who actually reply
In most practices the doctor is not the one monitoring reviews, which means compliance depends on whoever does. A front-desk staffer or a marketing contractor replying without training is where many violations begin, so the workflow only works if the people using it understand the rule.
Make the boundary explicit to everyone with access to your profiles: no reply ever confirms that a person was a patient, and no reply ever mentions care, dates, or payment, full stop. Give them the approved template and the check-list, and make clear that a delayed reply is always better than a risky one. It also helps to designate a single owner for review responses, so replies are consistent and one trained person carries the responsibility rather than anyone with the password improvising. If you use an outside agency, confirm in writing that they follow the same rule, because you remain responsible for what is posted under your practice's name. A brief, clear internal policy, understood by everyone who might click reply, is cheaper than any settlement and is the real safeguard.
Where to start
The safest habit is to decide your review-response policy before you ever get an angry review, not in the heat of one. A single reusable, generic template, applied calmly every time and never improvised by a frustrated staff member, protects your license and usually reads better to future patients than any defense of the facts. Pair it with a steady flow of honest reviews, and one bad review stops being a threat.
The Free Audit checks how your practice appears across Google, AI assistants, and 6 directories, scores you on the 7 pillars including your reviews and rating, and shows exactly which gaps to close first. It takes about 90 seconds and needs no signup for the free score.
Run your free audit at thedocmirror.com
By the The Doc Mirror team